🚨 FBI ISSUES CYBERSECURITY ALERT: FBI Sounds Alarm Over ARTEX AI Hacking Tool Used in Cyberattacks Against Global Organizations
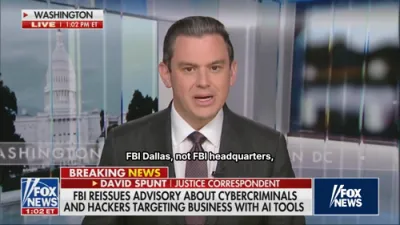
The FBI has renewed its warning about ARTEX, an artificial intelligence-powered hacking framework that cybercriminals and state-aligned threat actors are allegedly exploiting to automate cyberattacks against organizations worldwide. In a November 17 warning shared by its Dallas field office, the bureau highlighted the growing threat posed by the technology, which can automate multiple stages of a cyber intrusion with limited human involvement. According to an FBI FLASH advisory originally issued on November 13, ARTEX has been used in malicious campaigns since at least August 2026, targeting organizations in sectors including finance, government, technology, defense, energy, healthcare, manufacturing, and telecommunications. The framework can reportedly help attackers move from initial reconnaissance and targeting to privileged network access in under three hours. That speed gives cybersecurity teams significantly less time to identify suspicious activity and stop an intrusion before attackers gain deeper access to sensitive systems. The FBI also warned that ARTEX can enable relatively inexperienced hackers to conduct complex attacks against multiple organizations simultaneously.
The threat is not merely theoretical, as the FBI advisory identifies previous campaigns involving financial institutions in South Korea and a supply-chain compromise affecting ConnectWise Cloud Backup customers. In the ConnectWise-related campaign, attackers used the framework to pursue access to Microsoft 365 environments belonging to downstream customers, demonstrating how a single compromised service can create risks for numerous organizations. Although the original ARTEX developer reportedly removed the public repository in October, the FBI says modified versions, archived copies, community forks, and a commercial edition remain accessible to threat actors. The warning comes amid reports of disruptions affecting banks, airlines, and other digital services, but the FBI has not established a connection between ARTEX activity and the recent ground stop or other reported outages. The bureau is urging organizations to strengthen access controls, secure internet-facing applications, monitor unusual automated activity, and investigate unexpected changes to accounts and network permissions. With AI-driven tools accelerating the pace of cyber intrusions, the latest alert underscores the growing challenge of defending critical business and government systems against increasingly automated attacks.